8:30 – 9:00
Registration
9:00 – 9:15
Welcome to NSSS:
Beyond Compliance – Building Resilience
9:15 – 10:00
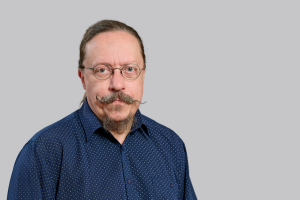
Keynote: Surviving in the new world
– Patrik Fältström, Netnod
10:00-10:30
To be announced
10:30-11:00
Tea break
11:00-11:30
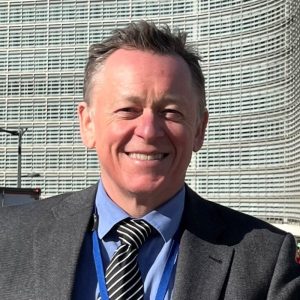
Market Surveillance for CRA
The presentation will include some general observations on how the market control activities will proceed as well the current status of praparation in Sweden and lessons learned so far with market control of the Cybersecurity articles in the RED
11:30-12:00
AI-assisted vulnerability finding with frontier models: the good, the bad, the ugly
The Eclipse Foundation has been in Anthropic’s Project Glasswing since its launch, using a frontier model to hunt vulnerabilities across a large open source code base. A first-hand account of what worked, what didn’t, what nobody wants to say out loud, and what it means for everyone shipping software under the EU Cyber Resilience Act.
12:00-12:30
KeyFactor
TBD
12:30-13:30
Lunch
13:30-14:00
Tureen
Product Security Comes of Age
Product security is undergoing a rapid process of formalization, driven an uptick in legislation and standardization. As a result, we’ll be able to communicate more clearly on security concerns, and products can be expected to become more secure overall. Well-established practices, such as those shared by several OWASP projects have existed for years but are now reaching a broader audience because they provide practical structure in an increasingly regulated environment. This talk explores how regulation, standards, and community-driven best practices converge, and how shared knowledge can help organizations collectively raise the baseline of product security rather than treating compliance as an isolated exercise.
14:00-14:30
sbomify
Getting SBOMs Right: A Practical Framework
SBOMs are quickly moving from best practice to baseline requirement, driven by regulations like the EU Cyber Resilience Act, U.S. Executive Order 14028, PCI DSS 4.0, and updates to the NIST Cybersecurity Framework. Yet most organizations still struggle with inconsistent tooling, shallow metadata, and a lack of validation standards.
This talk introduces a practical, six-phase framework for generating SBOMs that are accurate, enriched, and verifiable. It’s built on real-world implementation experience and informed by research currently under review by CISA. The framework is tool-agnostic and designed to scale, from single applications to large CI/CD environments.
14:30-15:00
Secure-by-Design: Automating Compliance and Evidence
As many teams navigate the evolving regulatory landscape across Europe (and beyond) affecting the supply chain, the mandate for “Secure-by-Design” has evolved from a best practice into an essential feature to ensure that digital products are secure and resilient.
While the principles of secure-by-design are widely understood, the operational reality of enforcing, verifying, and maintaining these postures at scale across the supply chain remains a significant hurdle.
This talk explores the critical gap between conceptual security design and measurable outcomes. It proposes a move from static documentation to capturing security decisions in machine-readable formats in order to support regulatory compliance and monitor supply chain resilience. It will also demonstrate how open-source projects and standards can provide the necessary infrastructure to implement these requirements.
15:00-15:30
Break
After the break, single track session
15:30-16:00
Keynote: Deluge, Distill, Defend: Mastering the AI Vulnerability Overflow
The current state of vulnerability finding and reporting with AI in Open Source and curl in particular. An autumn 2026 status recap. Where we are, where we might be going. The year the AI reports hit us for real.
16:00-17:00
Panel Discussion: Are we ready for the CRA?
A panel lead by Linda & Margarita with:
- Daniel Stenberg
- Olle E. Johansson
- James Christie, PTS
- Michaël Barbero, Eclipse Foundation
Conference partners

Organiser